
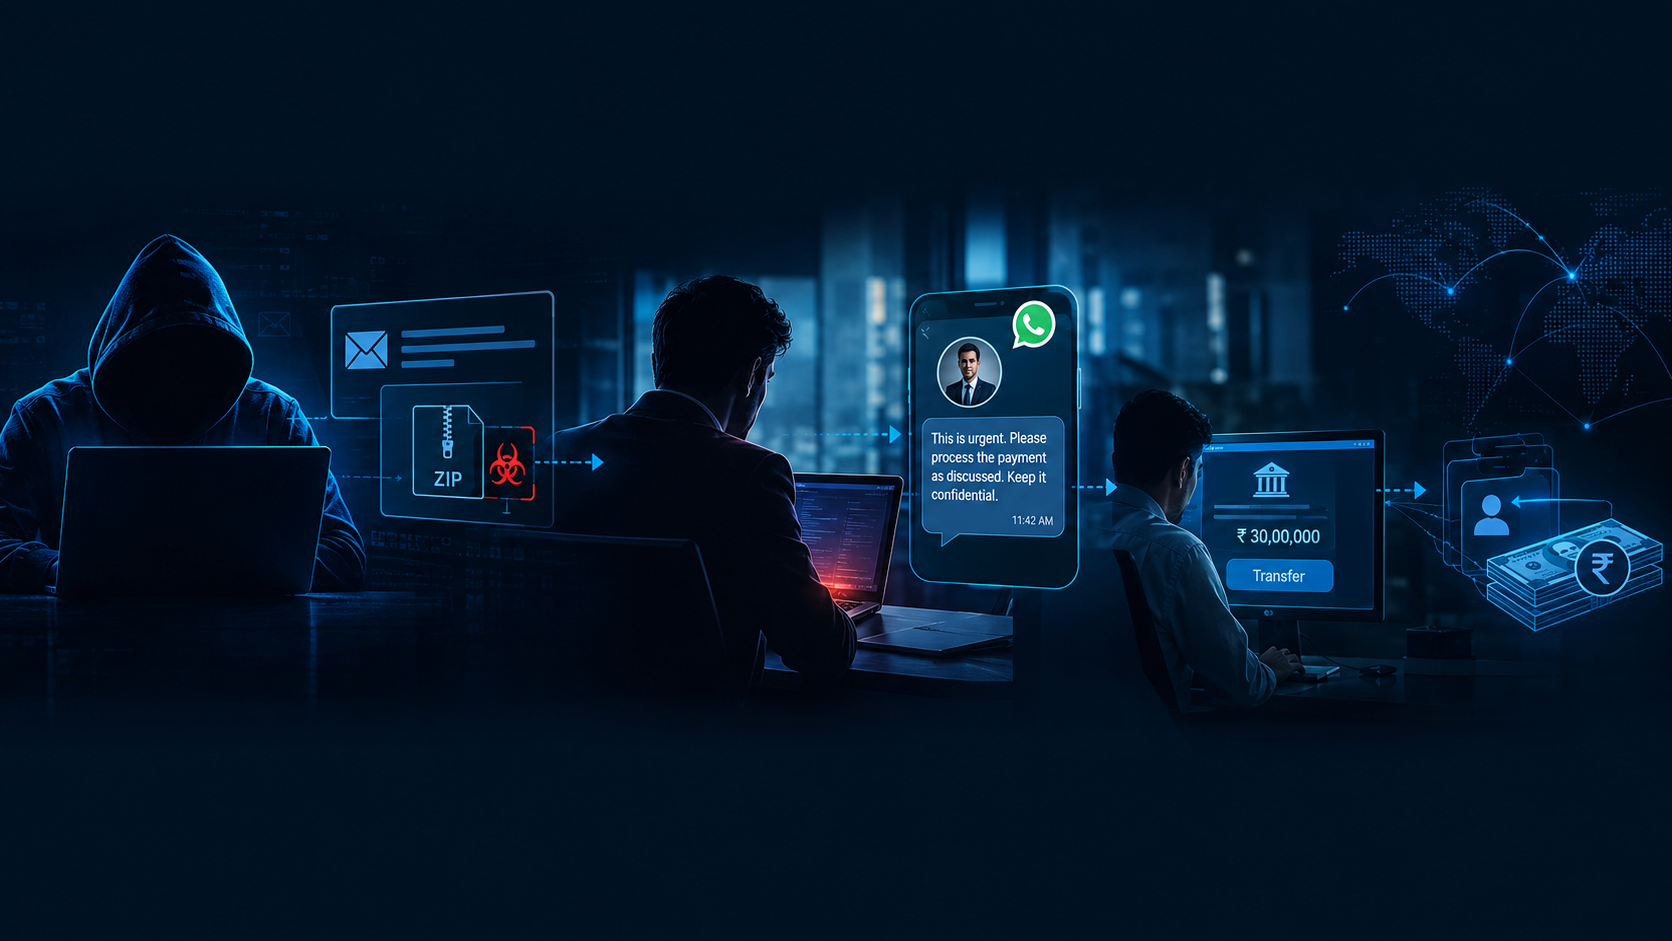
TechOwl Shield has analysed a live Windows banking-malware sample delivered over WhatsApp as a disk-image (.img) file, disguised as a bank statement or invoice with a message urging the recipient to open it on a computer and forward it to their finance team. We track the cluster internally as YOGI-IMG (antivirus family trojan.yogi); it is part of the India “Boss Scam” WhatsApp campaign reported by I4C and others.
The sample abuses a legitimately-signed binary to side-load a malicious DLL. That DLL is a first-stage downloader; the payload it fetches is what steals the money. What follows is the attack chain, the detection signals it produces, where attribution stands, and the controls that remove the largest parts of it.
Who is targeted
- Indian bank customers and — critically — finance teams, executives, and chartered accountants.
- Lures impersonate bank statements, invoices, “Reconciliation Confirmation,” KYC, and regulators (RBI, Ministry of Corporate Affairs).
- Delivery rides on trust: the file arrives from a known contact whose WhatsApp is already hijacked.
The attack chain
- Delivery over WhatsAppA file named like an invoice/statement (e.g.
D2_INV_<date>_v09.img) with a note to open it on a PC and forward it to finance — forcing desktop execution and spread into the money chain.T1566 · T1204.002 - Container + Mark-of-the-Web bypassThe file is an ISO 9660 disk image wearing a
.imgextension. Windows auto-mounts it and strips Mark-of-the-Web, so the “downloaded program” warning never fires. Inside: an invoice-named.exeandwebview_support.dll.T1553.005 - DLL side-loading via a signed binaryThe
.exeis a genuine, signed third-party “Webview Helper” (built on a well-known Chinese vendor's open-source UI framework). It is hard-wired to loadwebview_support.dllfrom its own folder; the attacker supplies a malicious DLL exporting the exact expected functions. No exploit, no vulnerability — the vendor is an abused third party, not a participant.T1574.002 - First-stage downloaderIn ~0.7 s the loader stages copies to
C:\Users\Public\<hex>\, runs the payload viarundll32.exe <dll>,MpayWebviewSupportMain, and downloads the next stage toC:\Users\Public\Documents\WU\c2b8.zip.T1218.011 · T1105 - The next stage is liveThe ~31 MB
c2b8.zipwas served (HTTP 200) at analysis time and is VirusTotal-malicious. It carries the remote-control / stealer capability; a real victim would receive it.next stage - Business email compromiseOn a decision-maker's machine the operator hijacks WhatsApp, impersonates the executive, and instructs finance to wire funds to mule accounts, reading the OTPs and approval messages along the way. Reported losses in this campaign reach ₹2.45 crore.T1534 · T1657
The decrypted C2 protocol
The downloader talks HTTP over TLS with User-Agent GeneratorApp/1.9.44, resolving its network (WinHTTP) and crypto (bcrypt) APIs at runtime and keeping its config encrypted — deliberate anti-analysis:
GET /sys/<build>/1/c2b8.zip                         ← next-stage payload pull
GET /r/<build>/download_fail?run_id=<YYYYMMDD-HHMM>  ← status callback
Observed execution timeline (Procmon)
08:50:40.869  INV-No.202608170.exe   Process_Start   loader starts
08:50:40.878  INV-No.202608170.exe   Load_Image      side-loads webview_support.dll (from ISO)
08:50:40.884  INV-No.202608170.exe   CreateFile      stages DLL+EXE -> C:\Users\Public\0F0236B4\
08:50:40.888  INV-No.202608170.exe   Process_Create  rundll32.exe "...\webview_support.dll",MpayWebviewSupportMain
08:50:40.897  rundll32.exe           Load_Image      loads the staged payload DLL
08:50:41.609  rundll32.exe           WriteFile       next stage -> C:\Users\Public\Documents\WU\c2b8.zip
Infrastructure and scale
Pivoting from the live C2 revealed an industrial operation, not a one-off:
- ~646 related samples communicating with the campaign's C2 domains (hundreds unique).
- 6 C2 base domains + ~13 subdomains across
.imgand.vbsdelivery stages. - Two dedicated hosting blocks on a single VPS provider (ASN 14956), a shared payload (
webview_support.dll), and rotating side-load DLL disguises (libvlc.dll,lua51.dll,pcaui.dll…). - Disposable, fast-rotating registration: every C2 domain is under 3 months old; several are DGA-flagged. Registrar suspensions on the older
.vbs-stage domains show the operator being partially taken down and pivoting to the still-live.img-stage C2s.
Attribution
There is no named group behind this. It is an unnamed, financially-motivated cybercrime cluster (family trojan.yogi; the India “Boss Scam” campaign). Infrastructure naming points weakly toward a Chinese-speaking operator, at low-to-medium confidence: naming can be misdirection and is not, on its own, attribution. The tooling is commodity-grade but well-run, with no zero-days but effective signed-binary abuse, staged delivery, encrypted C2, and disposable infrastructure. It is distinct from the Brazilian WhatsApp bankers (Water Saci, TCLBANKER, Astaroth) and from Android KYC-lure campaigns.
Why banks specifically must care
- It abuses your brand (fake statements, KYC, RBI/MCA notices).
- It targets both your customers and your own finance and leadership staff.
- It defeats conventional controls: a signed binary, no exploit, social engineering, encrypted C2.
- The outcome is direct account drain and fraudulent wire transfers.
A bank statement or invoice that arrives over WhatsApp as a file to open on a PC should be treated as an attack on the finance team, not as a document.
Guidance for customers and staff
Detection and hunting
Atomic indicators (domains, hashes) rotate weekly, so detect the behaviour. The highest-fidelity signal:
A signed EXE side-loading an unsigned DLL from its own directory on a mounted or removable volume, followed by rundll32.exe <dll>,<export> and an outbound beacon to a newly-registered domain.
Also hunt: ISO/.img mounted from a download or chat path; process staging to C:\Users\Public\<hex>\; a non-browser process reading WhatsApp or browser session stores; downloads to C:\Users\Public\Documents\WU\.
Recommendations
For bank customers
Banks never send statements, invoices, or KYC as .img, .exe, or .zip over WhatsApp. Don't open, don't forward, delete. Warn the sender that their account may be compromised.
For bank staff and executives
Treat any payment instruction arriving via chat as unverified until confirmed on a second channel — a call to a known number. This defeats the fraud even if the malware succeeds.
For bank security teams
- Block the indicators below and deploy the behavioural rules.
- Disable or monitor ISO/
.imgauto-mount and execution from mounted volumes where feasible. - Brief executives and finance teams specifically — they are the named targets.
- Report activity to CERT-In ([email protected]).
Indicators of compromise
Defanged. Campaign infrastructure rotates rapidly — re-validate before operational use.
Files (SHA-256)
| SHA-256 | File | Role |
|---|---|---|
de0ee4ef057a549f6ad9c819bda80f5e7d04c18006b2159f066f2dec68e8ced0 |
D2_INV_20260918_v09.img | ISO container (sample) |
ac638090f39f6343b1dc8673ae88c5b6a19e858a70da8435a73dcb7a6d239b38 |
INV-No.202608170.exe | signed side-load carrier (abused) |
52ed5616a373bafe93c9c60a91010cf1e00be9903c67648e7a0c5e7a95f23c39 |
webview_support.dll | malicious downloader |
2664bc8354a564b06a49a2bf31d639ee5fbfa7759d4ad0fd25d6f52a4008da6b |
A_INV_20260918_v08.img | sibling dropper |
webview_support.dll imphash 3f1cc480338ca4e30b60e544af966322 |
||
C2 domains
| Domain | Role | State |
|---|---|---|
vip[.]tiantianxiazai88[.]com |
primary .img C2 (beacon) | live |
tiantianxiazai88[.]com (+www/bbs/i/putong) |
.img C2 | live |
wantiyou[.]wiki (+putong/a1/aaa/hhh) |
parallel .img C2 | live |
cjian616[.]top (+api/cdn/jb/up) |
VBS C2 | live |
xiazaixitong8[.]com |
VBS C2 | suspended |
baoxissde[.]one |
VBS C2 | suspended |
mywwjj[.]xyz |
VBS C2 | suspended |
IPs — ASN 14956 RouterHosting LLC
| IP | Block | Hosts |
|---|---|---|
172[.]86[.]80[.]66 / .106 / .163 |
172[.]86[.]80[.]0/24 (SG) | tiantianxiazai88 / wantiyou subdomains |
45[.]59[.]120[.]50 / .13 / .116 |
45[.]59[.]120[.]0/24 (AE) | tiantianxiazai88, cjian616, baoxissde, mywwjj, wantiyou |
Excluded (shared hosting, not actor): 172[.]232[.]24[.]161/235, 172[.]234[.]25[.]42, 146[.]190[.]81[.]99 |
||
Network & host artifacts
| Indicator | Meaning |
|---|---|
hxxps://vip[.]tiantianxiazai88[.]com/sys/<build>/1/c2b8.zip |
next-stage payload (~31 MB, live) |
/r/<build>/download_fail?run_id=<YYYYMMDD-HHMM> |
C2 status callback |
User-Agent GeneratorApp/1.9.44 |
downloader UA |
Mutex Global\NEWorkGate |
payload single-instance |
C:\Users\Public\<8-hex>\ |
staging directory (loader + DLL) |
C:\Users\Public\Documents\WU\c2b8.zip |
next-stage download destination |
sconfig.dat, UEMSAgent.msi, setup1.vbs |
config / RMM-masquerade / VBS component |
Filename patterns: <X>_INV_<date>_v<NN>.img|.iso, <X>_pcalua_<date>.img, <X>_vlc_<date>.img, Statement of Account*, Bank Statement*.vbs, E-statement*, Reconciliation Confirmation Letter.img.


