1. Summary
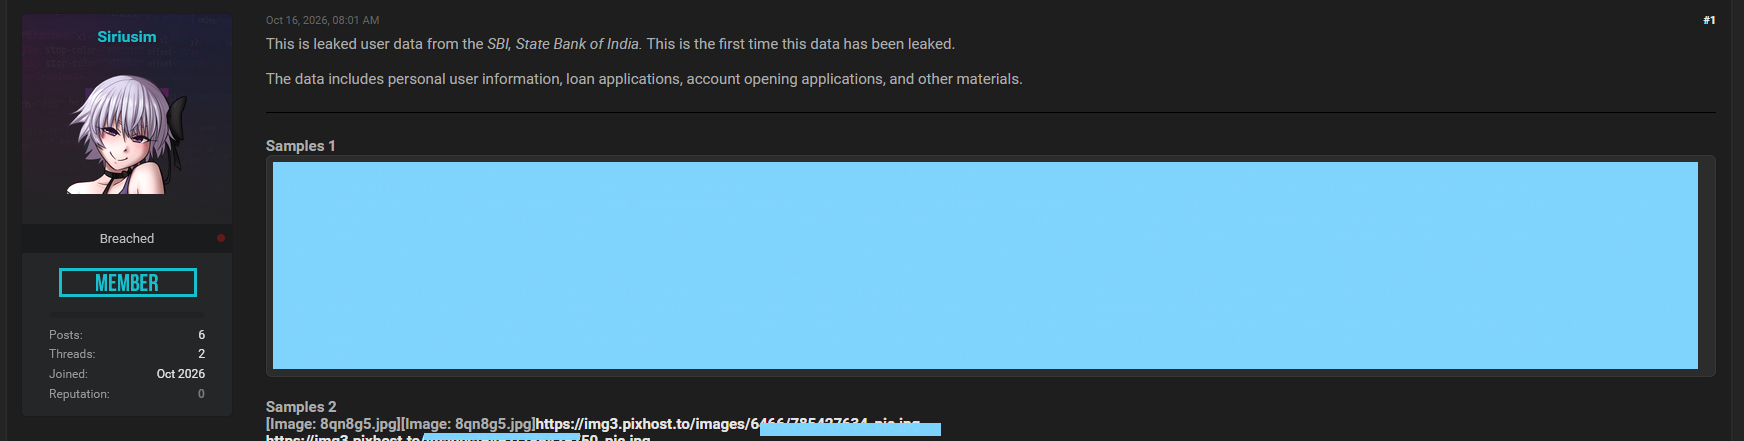
- 2026-10-16 08:01: actor "Siriusim" posted SBI customer data on a BreachForums instance: 375,000 CSV rows and 2,722 PDFs, with samples.
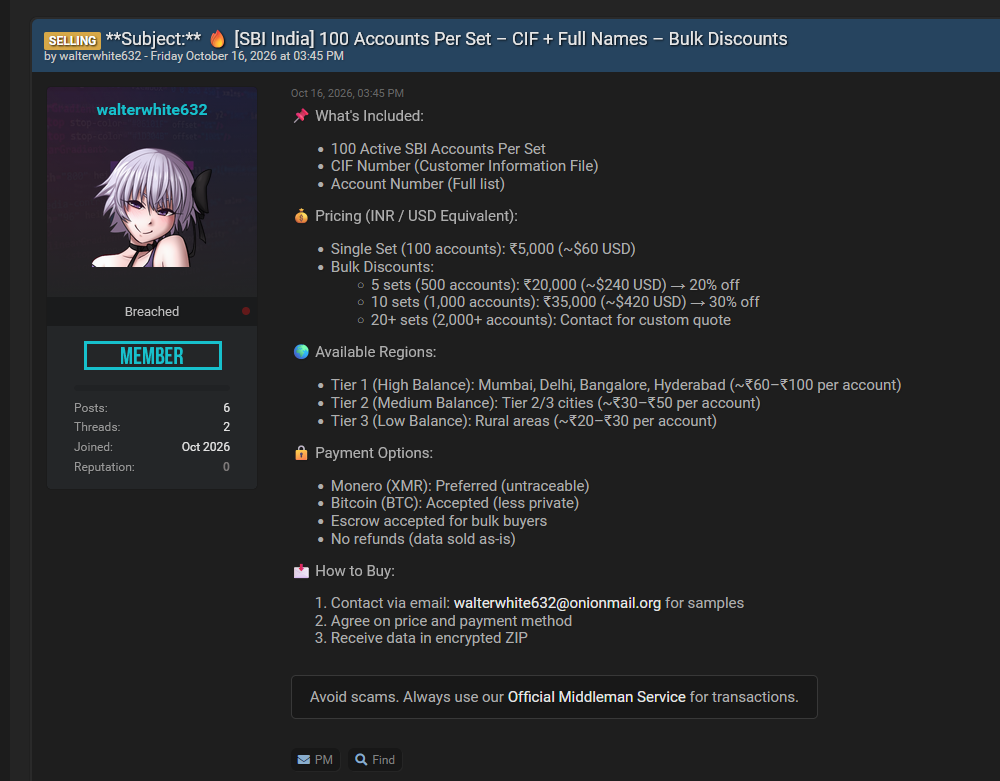
- 2026-10-16 15:45: actor "walterwhite632" advertised SBI "CIF + account number + name" sets for private sale.
- The data was extracted on 2026-10-10 at about 06:52 from SBI's video-KYC digital account-opening system. The PDFs are scanned loan-application forms.
- Stolen SBI staff credentials rose sharply from September 2026, including single sign-on and credit-bureau portal logins, with captures continuing to 2026-10-18.
Claimed rows
375,000
PDF documents
2,722
Confirmed by SBI
3,897
per press reports
Extraction
10 Oct 06:52
2. The leaked data
| Item | Finding | Confidence |
|---|---|---|
| Source system | Video-KYC digital savings-account onboarding | High |
| Second source | Scanned retail loan-application forms | High |
| Extraction | Scripted bulk extraction, 2026-10-10 ~06:52 IST* | High |
| Data freshness | Applications created 2026-10-08 to 10; live-system access | High |
| Authenticity | Genuine records from branches across several states | High |
| Targeting | Filtered to one application stage (053) |
Medium |
| Access type | Staff, agent or vendor-side access | Medium |
| 375k vs 3,897 | Rows do not equal unique customers | Medium |
The records also expose video-KYC session tokens and, for some applicants, CKYC numbers.
3. Threat actors
| Siriusim | walterwhite632 | |
|---|---|---|
| Posted | 2026-10-16 08:01 | 2026-10-16 15:45 |
| Type | Leak with samples | Private sale (email, XMR/BTC) |
| Profile | Joined Oct 2026, 6 posts, 2 threads, reputation 0 | Identical, including avatar |
Assessment
One operator running a leak-then-sell pattern.
4. Stolen SBI staff credentials
A separate exposure. A link to the leak has not been established.
- Credential theft from SBI staff rose sharply from 2026-09-09 and continues to 2026-10-18.
- Infections are concentrated on unmanaged or shared machines holding several staff and role accounts. Some are repeatedly reinfected, most recently on 2026-10-14 to 18.
- The credentials are being resold through Telegram "log cloud" channels.
Targeted assets (Aug–Oct 2026)
| Severity | Endpoint | Function | Last seen |
|---|---|---|---|
| Critical | adfs.sbi.co.in |
Federated single sign-on | 2026-10-18 |
| Critical | login.microsoftonline.com (SBI tenant) |
Microsoft 365 | 2026-10-18 |
| Critical | sso.sbi.co.in |
SSO portal | 2026-10-18 |
| Critical | myworkspace.sbi.co.in |
Remote workspace | 2026-10-10 |
| High | hub.crifhighmark.com, cir.crifhighmark.com |
Credit-bureau inquiry (third party) | 2026-10-18 |
| High | crcf.sbi.co.in |
Applicant-facing journey | 2026-10-18 |
| High | ems.sbi.co.in |
Internal staff application | 2026-10-17 |
| High | itnp.sbi.co.in |
Internal staff application | 2026-10-10 |
| Medium | emm.sbi.co.in |
Mobile-device management | 2026-09-12 |
| Medium | erupee.sbi.co.in |
Digital-rupee wallet | 2026-09-30 |
| Medium | hrms.onlinesbi.com, corp.onlinesbi.com |
HR and corporate banking | Aug–Oct 2026 |
| Low | egyanshala.sbi.co.in, mybanklearning.sbi.co.in |
Staff e-learning | 2026-10-18 |
5. Malware and delivery
Infected machines
195
with host details, Aug–Oct 2026
Loader-staged
50%
numbered %TEMP% task folders
One payload name
55
machines ran
4BtqZz1.exeNo AV / Defender only
97%
no enterprise EDR seen
Infection chains
| Chain | Machines | Assessment | Confidence |
|---|---|---|---|
Loader task folders: payloads in %TEMP%\<11 digits ending 0101>\, folder numbers rising steadily over time (12818950101 → 13714450101) |
97 | A single loader botnet issuing numbered download tasks; consistent with an Amadey-style loader pushing an infostealer | Medium |
IExpress droppers: %TEMP%\IXP###.TMP\<hex>.exe |
52 | Self-extracting stealer droppers, common in commodity stealer delivery | High (technique) |
| Fake or cracked software: Photoshop 2026, Creative Launcher 2026, "NexomiaUI", "[email protected]", run from Downloads, Desktop or inside RAR/7-Zip archives | 13 | Users downloading pirated software on machines that also hold SBI logins | High |
Script-based loaders: AutoIt3.exe in a random %TEMP% folder; Inno Setup is-*.tmp |
2 | AutoIt or installer-wrapped stealer loaders | Medium |
Random executables in the user profile (e.g. %USERPROFILE%\4mZbF5Dj.exe) |
10 | Second-stage drops | Medium |
Malware identified
| Role | Malware | Basis | Confidence |
|---|---|---|---|
| Loader | Amadey | Numbered task folders in %TEMP% (…0101) with a steadily rising task counter across victims; downloaded payloads renamed to 10-character hex names (f269bcb6e9.exe) |
Medium |
| Dropper packaging | IExpress self-extracting archives | %TEMP%\IXP###.TMP\ execution paths |
High |
| Infostealer payload | Lumma, StealC or Vidar (the stealers Amadey most commonly deploys) | Credential, cookie and browser-data theft delivered through the Amadey chain; family not distinguishable without samples | Low |
| Lure-delivered stealers | Fake cracked software: Photoshop 2026, Creative Launcher 2026, NexomiaUI, Setu@ | Executed from Downloads, Desktop or inside archives | High (delivery), family undetermined |
| Script loader | AutoIt-based loader | AutoIt3.exe in a random %TEMP% folder; a pattern used by Lumma and DarkGate campaigns |
Low |
File hashes from the infected machines will confirm the stealer family.
Malware IOCs
| Type | Indicator |
|---|---|
| Path pattern | %LOCALAPPDATA%\Temp\1[23]\d{7}0101\*.exe |
| Path pattern | %LOCALAPPDATA%\Temp\IXP\d{3}.TMP\[0-9a-f]{6}.exe |
| Path pattern | %USERPROFILE%\[A-Za-z0-9]{3,8}.exe (executables in the profile root) |
| File name | 4BtqZz1.exe |
| File names | f269bcb6e9.exe, dec1cc8707.exe, 687f121b84.exe, 2e03252ead.exe, ae0842df23.exe, 06bdb0b489.exe, 5d1eec84ad.exe, f7ac51d54c.exe, fc76062812.exe, 2f746185a8.exe |
| Lure names | Photoshop.2026.exe, Creative.Launcher.2026.exe, NexomiaUI_v9.77.998.exe, [email protected] (in Downloads\Compressed\Lastest_version\), Loader.exe |
| Loader artefacts | AutoIt3.exe in a random-named %TEMP% folder; %TEMP%\is-*.tmp\*.exe |
| Distribution | Telegram log clouds: ArtHouse Cloud, Arhont, CashFlow Premium Cloud Logs, Xavier_Log, PIXELCLOUD |
6. Victim surface and targeting
Who was infected
- Unmanaged devices. 63% of infected machines use default retail names (
DESKTOP-*,LAPTOP-*) and generic profiles (Admin, Dell, HP, user), the signature of personal, home or shop-bought PCs rather than bank-managed endpoints. - No enterprise protection. Almost all ran Windows Defender alone or no antivirus.
- Shared use. Several machines hold many staff and role accounts at once, and some are reinfected repeatedly.
- Peak in September. 45 infected machines in August, 115 in September, 35 in October to date.
What was targeted
Surfaces exposed, most to least frequent (Aug–Oct 2026):
- Identityadfs.sbi.co.in · sso.sbi.co.in · Microsoft 365
- Applicant journey portalcrcf.sbi.co.in
- Internal staff applicationsems · itnp · myworkspace · emm · hrms
- Staff e-learningegyanshala · mybanklearning
- Credit-bureau inquiry portalhub.crifhighmark.com · cir.crifhighmark.com
- Personal and third-party sites using SBI work identities
- Digital rupee, business banking, mutual fundserupee · yonobusiness · sbimf
Infostealers take everything saved in the browser, so this reflects what staff log into from these machines, not a choice the attacker made. The concentration on identity and applicant-facing systems is what makes it critical: stolen SSO credentials and session cookies open the rest.
7. Timeline
From infection to leak
August to October 2026
- Staff machines infectedAug 2026
- Credential theft spikesfrom 2026-09-09
- Applications created2026-10-08 to 10
- Data extracted2026-10-10 ~06:52
- Repeat infections at one office2026-10-14 to 18
- Siriusim leak posted2026-10-16 08:01
- walterwhite632 sale posted2026-10-16 15:45
- CERT-In alert; SBI confirms 3,897 records2026-10-16 to 20
- Siriusim thread no longer found2026-10-21
8. Indicators
| Type | Indicator |
|---|---|
| Actor handles | Siriusim, walterwhite632 |
| Contact email | [email protected] |
| Forum | BreachForums instance at bf.st |
| Sample hosting | img3.pixhost.to |
| Malware | See section 5 |
| Hunting anchors | Lead-ID prefix SBIY2RYC, stage 053, 2026-10-10 06:00–08:00 IST |