SocksEscort Takedown: AVrecon Botnet Analysis and Banking Fraud Impact
TechOwl ShieldMarch 18, 2026
Executive Summary
Overview
On March 12, 2026, an international law enforcement operation codenamed Operation Lightning dismantled SocksEscort — a criminal proxy service that routed fraud traffic through compromised residential routers to bypass bank fraud detection systems. The service powered account takeovers, credential stuffing, and financial fraud that cost victims millions of dollars.
While the operation seized 34 domains, 23 servers, and froze $3.5 million in cryptocurrency, our analysis shows the takedown was partial — the operators remain unidentified, hundreds of thousands of infected devices persist, and the underlying malware infrastructure can be rebuilt.
SocksEscort was not a generic cybercrime tool — it was specifically used for financial fraud. Court documents and the FBI FLASH advisory (20260312-001) confirm:
CONFIRMED FINANCIAL FRAUD ACTIVITY
Bank account takeovers using stolen credentials routed through residential IPs
Cryptocurrency exchange theft — a New York victim lost $1 million
Business payment fraud — a Pennsylvania manufacturer defrauded of $700,000
Military financial accounts — $100,000 stolen via Military Star cards
Fraudulent unemployment insurance claims processed through financial institutions
Password spraying campaigns targeting Microsoft Outlook and enterprise services
How It Defeats Bank Fraud Controls
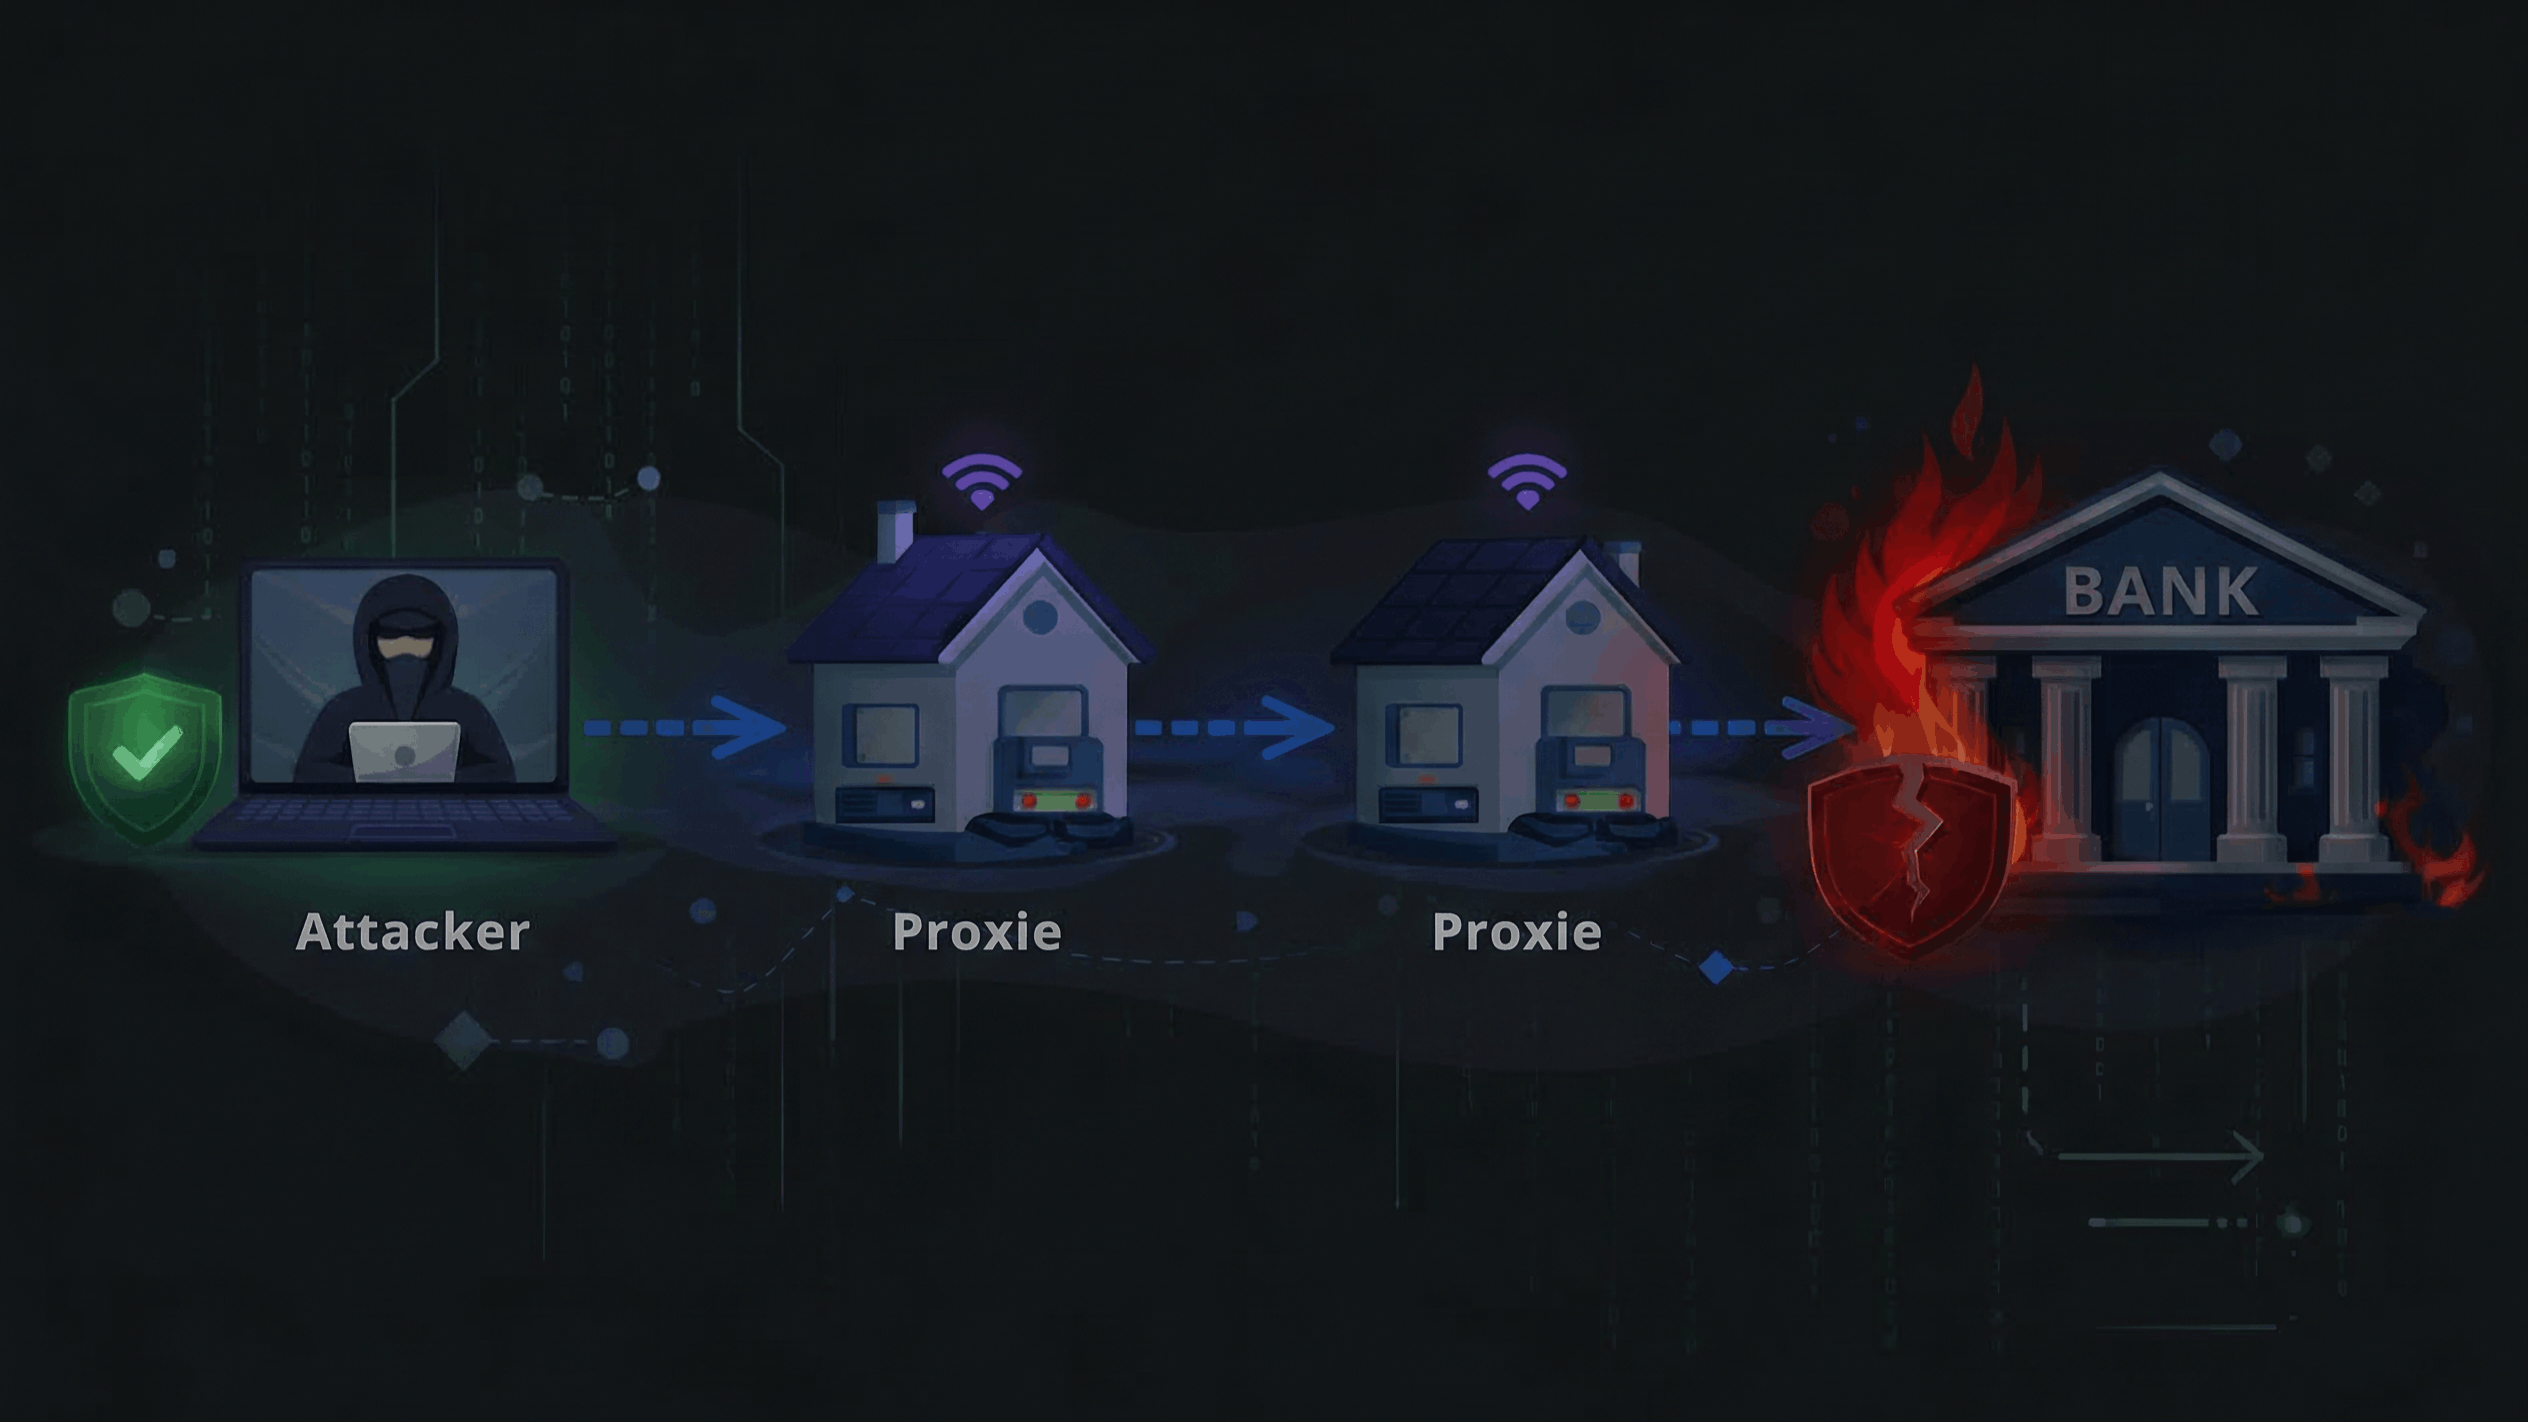
Residential proxy botnets make criminal traffic indistinguishable from legitimate customer activity at the network layer:
Fraud Control
Without Proxy
With SocksEscort
IP Reputation
Blocked — VPN/datacenter IP flagged
Passes — legitimate residential ISP
Geolocation
Flagged — foreign IP, impossible velocity
Passes — same city/region as account holder
ASN Filtering
Blocked — known hosting/proxy ASN
Passes — consumer broadband provider
Rate Limiting
Triggered — multiple attempts from same IP
Evaded — each attempt from different residential IP
SocksEscort proxy chain: criminal traffic exits through a compromised residential router, making it indistinguishable from legitimate customer access at the bank's fraud engine.
Technical Analysis
The Malware: AVrecon
SocksEscort's proxy network was powered by AVrecon, a Linux-based Remote Access Trojan (RAT) written in C that targets small-office/home-office (SOHO) routers and IoT devices.
Attribute
Detail
Source
Language
C
FBI FLASH
Target Architectures
MIPS (Big Endian), ARM (Little Endian), MIPSEL
FBI FLASH
Targeted Device Models
~1,200 models from Cisco, D-Link, Hikvision, MikroTik, Netgear, TP-Link, Zyxel
Firmware persistence — Flashes custom firmware containing AVrecon, hardcoded to execute on startup. The modified firmware disables update and flashing features, making the infection permanent.
Non-persistent deployment — Runs in memory without persistence. A power cycle clears the infection. However, C2 servers have been observed re-infecting devices using the same original vulnerability.
Command and Control Architecture
AVrecon uses a tiered C2 architecture:
Tier
Function
Details
TIER 1
First-stage C2 domains
Embedded in malware binary. Initial beacon target.
TIER 2
Second-stage C2 servers
~15 active at any time. PING/PONG heartbeat every 60s on port 8000.
TIER 3
Management infrastructure
Aggregates data from all second-stage servers.
When a C2 server has tasking, it interrupts the heartbeat loop and directs the router to open a SOCKS5 tunnel to a relay server. SocksEscort customers then route their traffic through the infected residential router.
AVrecon's tiered C2 architecture. Management tier aggregates from ~15 second-stage servers, which maintain PING/PONG heartbeats with ~20,000 infected routers weekly across 163 countries.
Custom X-Proto-* headers carry encrypted device reconnaissance data. The heartbeat protocol exchanges literal PING and PONG strings over port 8000.
Malware Artifacts
From our analysis of two AVrecon samples obtained from MalwareBazaar (verified against FBI FLASH and Black Lotus Labs hashes):
Component
Filename
Size
Architecture
Function
Loader
x
3,016 bytes
ELF 32-bit MIPS
Downloads and installs main RAT
Main RAT
dnssmasq
70,776 bytes
ELF 32-bit ARM
Full C2 communication, SOCKS5 proxy, device control
KEY BINARY FINDINGS
RAT masquerades as the legitimate dnssmasq DNS forwarder service
Checks port 48102 to detect existing infections before deploying
Stores C2 config in device nvram using variables domik, urlik, portik
Contains strings suggesting capability to change router admin passwords and disable firmware auto-updates
Uses D-Link-specific commands (xmldbc) for device identification
Internal codename: vilochka — matching Symantec's 2016 classification of this malware family
Infrastructure Analysis
C2 Hosting Providers
We enriched all 24 C2 IP addresses from the FBI FLASH against current ASN and geolocation data:
Hosting Provider
ASN
Location
C2 IPs
Risk Profile
velia.net
AS29066
Strasbourg, FR
5
Legitimate provider. Abused by operators since 2016.
Proton66 OOO
AS198953
St. Petersburg, RU
3
Known bulletproof hosting. Advertised as "100% bulletproof" on Russian cybercrime forums.
HZ Hosting Ltd
AS59711 / 61046 / 202015
AMS / London / Chicago
3
Multi-ASN operator.
M247 Europe SRL
AS9009
Hong Kong
2
Major VPN infrastructure provider.
Scalaxy B.V.
AS58061
Dallas, US
2
Dutch provider with US presence.
SERVERS TECH FZCO
AS216071
Amsterdam, NL
2
Dubai-registered. One IP has reverse DNS pointing to mail.socksescort.com.
PROSPERO OOO
AS200593
St. Petersburg, RU
1
Linked to Proton66. Same peering and IX.
Others
Various
DE / HU / NL
4
Mixed legitimate providers.
INFRASTRUCTURE EVOLUTION
The operators maintained infrastructure on velia.net from 2016 through 2026 — a 10-year hosting relationship. After Black Lotus Labs disrupted their C2 in July 2023, they added Russian bulletproof hosting (Proton66/PROSPERO), indicating deliberate escalation toward abuse-resistant infrastructure.
Passive DNS History
Using AlienVault OTX passive DNS, we reconstructed C2 domain resolution history not included in any public report:
zerophone.cc (registered January 2016 — oldest known C2 domain):
Period
Resolved IP
Provider
Location
Aug 2020 – Mar 2021
94.228.213.3
Unknown
Netherlands
Apr 2021 – Jan 2022
51.158.47.74
Scaleway
France
Aug 2023 – Dec 2025
62.138.0.211
velia.net
France
Mar 2026
Shadowserver sinkhole
Law enforcement
DE/NL
Multiple seized domains now resolve to Shadowserver Foundation sinkhole IPs — confirming active monitoring of infected devices still attempting to beacon.
Domain Registration Patterns
r0ck.online and evrc.space were registered on the same day (August 31, 2023) — seven weeks after the 2023 C2 disruption. Both initially resolved to 127.0.0.1 (localhost), indicating pre-staged reserve domains.
Operators used multiple registrars (Eranet, GoDaddy, PublicDomainRegistry) to avoid single-point takedown.
20 of 23 FBI FLASH domains use the .cc TLD. Non-.cc domains appeared only after the 2023 disruption — TLD diversification as an operational security response.
What the Takedown Did — and Didn't — Accomplish
Operation Lightning disrupted the service infrastructure but did not eliminate the botnet or apprehend the operators. Historical precedent shows they can rebuild within 24 hours.
Linked to Proton66; same operators per Intrinsec research
AS216071
SERVERS TECH FZCO
Hosted AVrecon C2 and SocksEscort infrastructure
Note: ASNs such as AS29066 (velia.net) and AS9009 (M247) are large, legitimate providers abused among many legitimate tenants. Flag specific IP ranges rather than blanket-blocking.
Residential Proxy Detection
RECOMMENDED COUNTERMEASURES
Residential proxy detection services (e.g., Spur.us, IPQualityScore) that fingerprint traffic routing through compromised residential devices
Behavioral analytics that detect session anomalies regardless of IP reputation — login timing, navigation patterns, transaction velocity, mouse/keyboard dynamics
Device binding with challenge-response — flag when a "trusted device" appears from a residential IP that also proxies other users
Endpoint and Network Security
For branch networks, ATM connectivity, and corporate infrastructure:
Audit network devices against the FBI FLASH targeted device list. Prioritize End-of-Life devices.
Monitor SOHO routers for outbound connections to C2 IPs and domains on ports 8000, 5178, and 8080.
Implement DNS sinkholing for the 23 confirmed C2 domains on internal resolvers.
Ensure firmware is current on all internet-facing network equipment — many SOHO devices do not auto-update.
For remote workforce:
Employees connecting via VPN through home routers among the 1,200 targeted models may unknowingly route traffic through compromised devices.
Provide guidance on router firmware updates and password changes for identified device models.